Local runtime
The malt CLI and daemon own local trust, keys, UnixFS application behavior, backup/sync orchestration, and verified payload exposure.
Keep keys and accepted roots on the user's device, authenticate structured relationships with malt-core, and treat gateways or peers as replaceable untrusted data sources.
Product boundary
MALT is a local data runtime that runs on the user's device. Its daemon is the primary long-running process, while CLI, future GUI, foreground mode, and local APIs share the same application and trust boundaries.
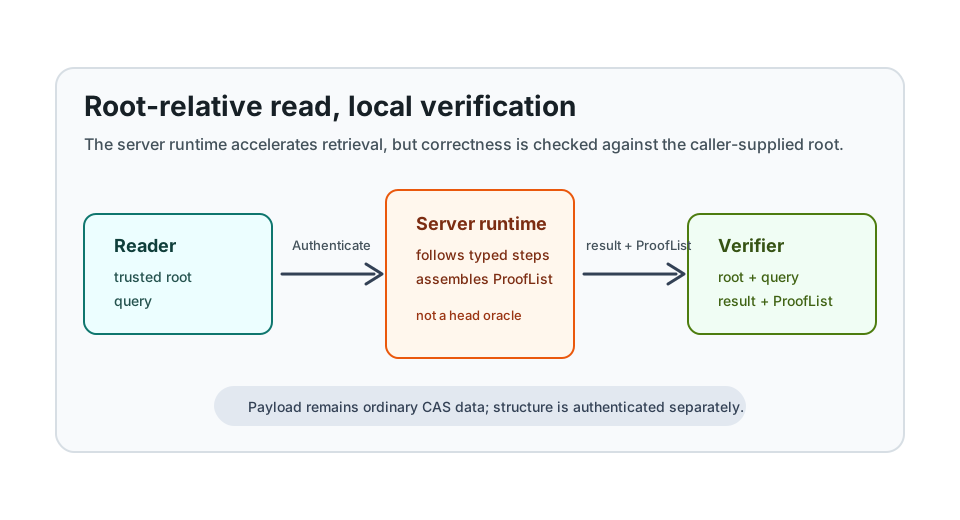
MALT Core authenticates graph-shaped relationships through opaque labels, Prefix and Positional trees, and Root-bound proofs. Payloads may live on local disk, in CAS, behind a Gateway, or in future peer transports; every remote proof and payload CID is checked locally before use.
A Gateway can accelerate execution and provide Bucket/CAS services. It is optional and untrusted: observed heads remain observations, candidate roots remain separate, and only local policy promotes an accepted root.